BNN Summary
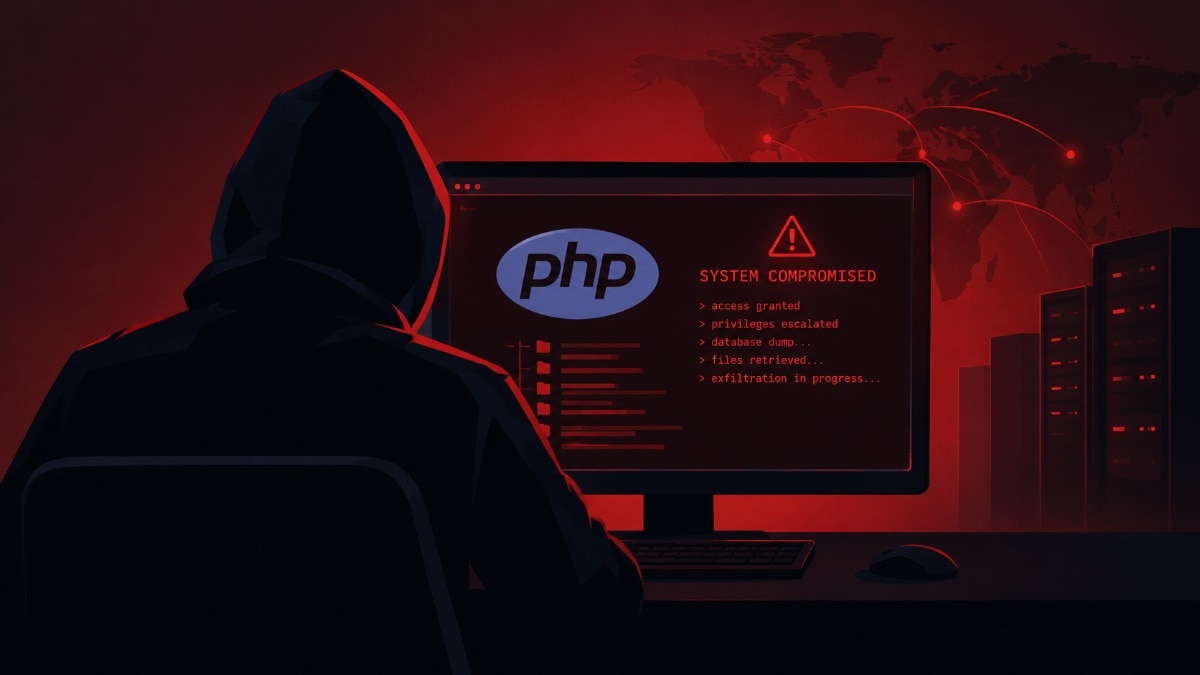
Cybersecurity agencies and software maintainers are urging system administrators to apply emergency patches following the discovery of severe remote code execution vulnerabilities in the PHP programming language. The flaws, collectively tracked in security advisories under identifiers such as PHP2Shell, allow unauthorized actors to hijack vulnerable web servers. Because PHP powers a vast majority of the modern web, immediate remediation is required across all enterprise environments.
In-Depth Analysis
The PHP development team has officially deployed urgent security updates across all supported release branches following the discovery of critical vulnerabilities capable of enabling unauthenticated remote code execution (RCE). Labeled across technical threat advisories and research publications as PHP2Shell, the high-severity security flaws pose an immediate danger to internet infrastructure due to the pervasive role PHP occupies across modern web ecosystems. Recent telemetry metrics indicate that PHP still powers upwards of seventy percent of all websites with known server-side programming languages, meaning that vulnerabilities of this caliber present high-value targets for both opportunistic cybercriminals and state-sponsored threat actors.
According to technical reports issued by cybersecurity research firm Qualys and ecosystem outlets including Laravel News, the newly patched vulnerabilities stem from improper input validation and unsafe argument handling within core interpreter components. In specific operating configurations—notably environments where PHP interacts with system-level command invocations, specific command-line interfaces, or legacy Common Gateway Interface (CGI) wrappers—attackers can inject arbitrary commands that the host operating system executes with the permissions of the underlying web daemon. This sequence allows an unauthenticated external adversary to bypass authentication barriers, deploy interactive command shells, manipulate databases, and compromise surrounding corporate network segments.
The global scope of the discovery has prompted warnings from international cybersecurity bodies and enterprise security teams, who caution that weaponized exploits are frequently published shortly after patch releases. Modern automated botnets rapidly incorporate proof-of-concept exploits to scan public internet ranges, targeting exposed web applications, e-commerce stores, enterprise portals, and popular content management systems such as WordPress and Drupal.
Framework maintainers and hosting providers have mobilized to assist downstream consumers in mitigating the fallout. Major web framework teams, including Laravel, published early notices advising infrastructure teams to schedule emergency maintenance windows to apply the upstream patches immediately upon release. Cloud platforms and managed hosting environments have begun rolling out fleet-wide runtime updates, though self-hosted and on-premise infrastructure setups remain dependent on manual intervention by system administrators.
To safeguard production environments, engineering organizations must immediately upgrade all production and staging workloads to the latest patched revisions across supported release series, including PHP 8.1, 8.2, and 8.3. Organizations operating legacy or end-of-life PHP versions—such as PHP 7.x or 8.0, which no longer receive official security patches—face elevated risk and must prioritize migration or isolate affected systems behind strict reverse proxies.
In addition to applying official packages, security practitioners recommend reviewing application configuration settings inside php.ini files. Best practices include disabling hazardous administrative functions such as exec, passthru, shell_exec, and system when they are not strictly required by application architecture. Security operations teams should also inspect server access logs for anomalous request signatures and enforce web application firewall (WAF) filtering rules to intercept exploit payloads before they reach the interpreter.
How do you feel about this story?
Discussion
No comments yet. Be the first to share your thoughts.
Join the discussion
Sign in to share your thoughts on this story.